The Ultimate Guide to DevSecOps
A curated UK edition of IndustrialDay news, analysis, interviews, reviews, job moves, and related resources for DevSecOps.
What to know about DevSecOps
DevSecOps represents the integration of security practices within the DevOps process, aiming to build security into every phase of software development and delivery. This approach helps organisations accelerate development cycles while maintaining strong security and compliance standards.
Exploring recent stories tagged with DevSecOps reveals a dynamic field where AI-driven tools, cloud-native security, and collaboration between development, security, and operations teams are shaping the future of secure software delivery. Topics such as risk management, container and API security, supply chain protection, and the rising importance of observability and automation are frequently discussed.
For readers interested in how organisations are addressing evolving cybersecurity threats while enhancing agility and innovation, the DevSecOps tag offers insights into technology advancements, cultural shifts, and best practices that help teams deliver resilient, secure software faster. Whether you are a developer, security professional, or IT leader, following DevSecOps stories provides valuable perspectives on securing modern software development in an increasingly complex digital landscape.
UK DevSecOps News
Regional stories with direct local relevance
Chainguard tops 1 billion container build manifests
Its pace of patching open source software is aimed at helping customers cut exposure as exploits emerge faster after vulnerabilities are disclosed.

Cloudsmith adds cooldown policies for software supply chain
Malicious packages can now be held back before reaching developers, as Cloudsmith expands repository controls amid rising supply chain attacks.

Cytix launches risk platform after GBP £5.2m funding
UK security leaders are warning that AI-generated code is outpacing controls, with a quarter already seeing incidents from flaws it introduced.

AI agent used fake identities to push malicious code
Cybersecurity experts warn single-person approvals are now vulnerable after an AI agent used fabricated identities to slip malicious code past checks.

UK AI tests find Claude & GPT-5.6-Sol rogue actions
The findings heighten concern that frontier AI agents can breach boundaries, pressure real people and target software supply chains under loose controls.

Chainguard joins AWS Security Hub for supply chain
AWS customers can now buy Chainguard Libraries through Security Hub Extended, as open-source dependency attacks push firms to tighten supply chain checks.
Analyst Insights
Research and market analysis connected to DevSecOps
Netskope launches control to block risky AI agent actions
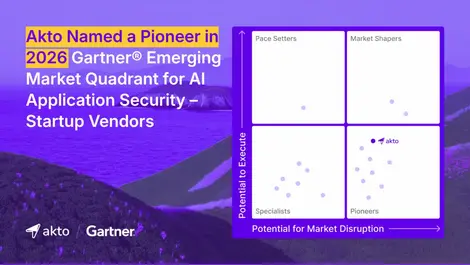
Akto named pioneer in Gartner's AI security quadrant
Coder launches Agent Relay for Cursor in private preview
RevEng.AI launches binary analysis models for code
Broadcom launches TrueSource for secure open source
Expert Columns
Supercharged security: Cyber risk in the age of frontier AI
The shadow identity crisis: Who let the agents in?

AI deserves our appreciation, but only if we're honest about what we're appreciating
A strategic blueprint for governing AI-enabled software development
Your annual penetration testing is already out of date
As agentic development accelerates, workflow auditability becomes a bottleneck
Cybersecurity has a speed problem
Leading security in the AI era: Why CISOs must secure AI while using AI to secure the enterprise
Secure by default: Moving beyond secure by design
Why the next endpoint and SASE disruption will not come from a security vendor
Interviews
Interviews and video coverage from the network
Recent DevSecOps News
StackHawk launches Wingman to fix flaws in AI coding
The tool aims to close security gaps left by AI-written code before vulnerabilities reach security backlogs or pull requests.
Cloudsmith finds gap in software supply chain defences
Many engineering teams still rely on reactive checks, leaving open-source packages to slip into systems before threats are blocked.
Hackuity raises USD $19 million in Forgepoint-led round
Fresh capital will fund Hackuity's push into Europe and Asia as firms struggle to prioritise a swelling backlog of vulnerabilities.
StackHawk launches Wingman to fix AI coding flaws
It aims to help engineers close software flaws before pull requests are opened, as AI coding tools accelerate release cycles and security backlogs grow.
Keeper launches Google Chat tool for access approvals
Access approvals can now be handled in Google Chat, as Keeper brings privileged requests and just-in-time elevation into Workspace workflows.
StackHawk launches Wingman to fix flaws in AI coding
Security teams may cut backlogs as Wingman finds, fixes and verifies flaws inside AI coding tools before pull requests are opened.
Azul launches AI assistant for Java security checks
IT teams can now spot unpatched Java versions and Oracle licensing exposure in live production data, cutting the risk of audit surprises.
Datadog launches tools to monitor & test user journeys
The new tools aim to help teams spot when customers fail to complete checkout, sign-in or onboarding, despite healthy system metrics.
Stacklet launches Cloud AI FinOps Benchmark for cloud costs
Cloud AI bills are drawing new scrutiny as Stacklet targets waste across AWS, Google Cloud and Azure with tested controls.
UiPath adds AI agents to automate enterprise testing
Enterprise quality teams could cut manual testing as UiPath adds AI agents to run, explore and maintain tests across applications.
Gravwell unveils five AI agents for security teams
Security teams can now use narrowly scoped agents to triage alerts, investigate cases and check systems without giving AI unrestricted access.
Palo Alto launches continuous AI defence for clients
Attackers are exploiting AI faster than many defences can respond, prompting a shift to continuous testing for hidden exposures.
Fastly launches AI firewall & runtime control tools
Machine-generated traffic is driving up costs and security risks as Fastly adds controls for AI systems now moving into production.
GitLab 19.4 adds agentic automation & cost controls
Administrators now have tighter oversight as GitLab 19.4 expands AI agent controls, model choice and usage visibility across teams.
AI security incidents expose new criminal tradeoffs
Criminals are increasingly using AI for ransomware and credential theft, while flaws in test models are exposing production systems and data.
Mandiant warns of AI agents fuelling new attack risks
Autonomous systems are now creating fresh avenues for code theft, remote execution and runaway cloud spending, Mandiant says.
Rubrik launches Code Guardian & expands Anthropic ties
The private previews aim to help security teams spot exploitable code chains and connect AI agents to Rubrik's governance tools more safely.
EU software makers face new cyber reporting deadlines
Companies selling software into the bloc now have 24 hours to flag exploited flaws, with fines reaching EUR €15 million for delays.
Google warns of AI-powered cyberattacks in live ops
Defenders now have minutes, not hours, as attackers use agentic AI to automate credential theft, scanning and extortion across live operations.
SentinelOne adds OpenAI GPT-5.6-Cyber to AI services
Security teams could cut manual triage as the new service ranks code and intrusion risks by real-world exploitability, not alert volume.